Kriton Agentic Security

It’s about time you take back control.

Agentic security and a policy engine inside your team’s Claude Code sessions.

Install our Claude plugin and give it a go!

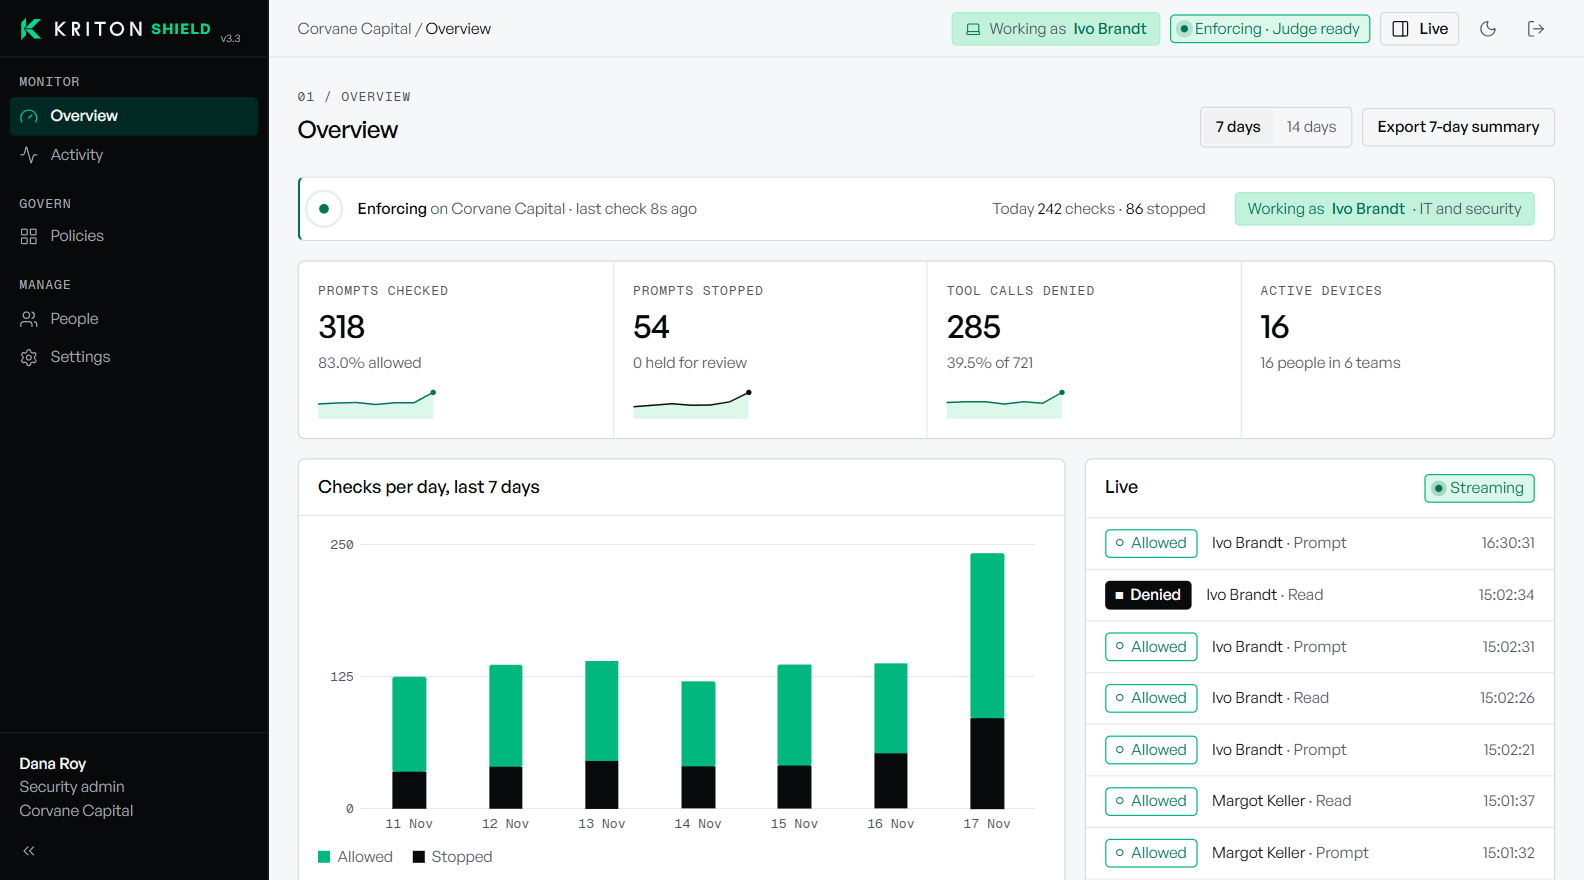
The Kriton Shield console Overview page in light mode, signed in as the security admin of a demo company: totals, checks per day and the live list of allowed and denied actions.
01The exposure

Your people run agents with no guardrails. One hidden line turns a helper into an insider.

  • Agents hold the keys.

    User agents, or personal agents, are intelligent agents that take action on your behalf. Bots can act on behalf of their creators to do good as well as bad.

  • Anyone can steer them.

    In the context of information security, social engineering is the psychological manipulation of people into performing actions or divulging confidential information. In social engineering, the attacker may pose as authority to increase the likelihood of adherence from the victim.

  • Nothing checks what it was told.

    Some systems may attempt to stop an intrusion attempt but this is neither required nor expected of a monitoring system.

02What you get

Two layers between your agents and your company. Both live today.

ALive now

Agentic security

Protection against agentic attacks and agentic CVEs.

A vulnerability is a weakness in a piece of computer software which can be used to access things one should not be able to gain access to. The Common Vulnerabilities and Exposures (CVE) system provides a reference-method for publicly known information-security vulnerabilities and exposures. CVE Identifiers give each vulnerability one different name, so people can talk about specific vulnerabilities by using their names.

Kriton checks every prompt against our own defensive RAG of agentic attacks and agentic CVEs, and we keep adding to it.

Defensive RAGMatched before the agent acts
  • Order hidden in an attached fileDenied
  • Tool output that rewrites the taskHeld
  • Agent told to post data outsideDenied
  • Ordinary request, nothing matchedAllowed
Examples of what the defensive library matches, and what Kriton does with each.
BLive now

Policy engine

Team rules your agents cannot talk their way around.

Policies are statements that bring together attributes to express what can happen and is not allowed. Within an organization, roles are created for various job functions. Members or staff (or other system users) are assigned particular roles, and through those role assignments acquire the permissions needed to perform particular system functions. The principle of least privilege forces code to run with the lowest privilege/permission level possible.

In the console’s Policies page you set, per team, which folders, files, company tools, databases and websites its agents may touch. Start with one team and one folder.

PoliciesEnforcing
PlaceLeadershipFinanceAdvisers
finance/FullFullClosed
hr/FullReadClosed
clients/FullClosedRead
CRMFullReadRead
Production databaseFullReadClosed
Outside websitesOpenClosedClosed
An example policy: what each team’s agents may touch.
03Install

Install in seconds.

  1. 01

    Your admin copies one command.

    In the console, each person gets an install command. It works once and expires after 15 minutes.

  2. 02

    Paste it in a terminal.

    It downloads the plugin, checks the download against its checksum and connects that laptop to your workspace.

  3. 03

    Start Claude Code.

    From the first session every prompt and every agent action is checked, and your admin watches it in Activity.

powershell -NoProfile -Command "& ([scriptblock]::Create((irm https://app.kriton.ch/i.ps1))) -Token ke_..."
curl -fsSL https://app.kriton.ch/i | sh -s -- ke_...
The install command for each system. The green ke_ part is where your admin's one-time code goes.

Needs Node.js 22 or later and Claude Code on the laptop. The ke_ code at the end comes from your admin and works once.

04The edge

Strike before the action runs. A log only tells you afterwards.

  1. With KritonThe agent asks Kriton stops itNever runsNothing to clean up
  2. With logs aloneThe agent asksThe action runsA log is writtenYou find out

A system that terminates connections is called an intrusion prevention system, and performs access control like an application layer firewall. Insider threats are harder to defend against than attacks from outsiders, since the insider already has legitimate access to the organization's information and assets.

The average breach takes 247 days to identify and contain (IBM, Cost of a Data Breach 2026). Kriton stops the action before it runs.

05The company

Find the weak point. Close it. Stay ahead of what comes next.

  1. 01

    Kriton Assessment

    By engagement

    We attack your agents before someone else does. When we find the vulnerabilities, we won’t just send you a PDF, we’ll fix it with you.

    Kriton Assessment in detail
  2. 02

    Kriton Shield

    Live now

    Agentic security and the policy engine, on every prompt and every agent action in Claude Code, live.

    Kriton Shield in detail
  3. 03

    Kriton Omni

    Coming soon

    Omnipresent agentic security against harness, agentic and adaptive attacks.

    Kriton Omni in detail
06Measured

Our numbers beside theirs. Every figure has its source.

See every number
Attacks caughtHigher is better
  1. Kriton ShieldKriton100%14 of 14 attack prompts, every one of 5 runs. Run file on request
  2. LLM GuardProtect AI99.7%Recall on 20,000 prompts. Source
  3. NeMo GuardrailsNVIDIA98.9%With three safety models, 215 in-house cases. Source
  4. Lakera GuardCheck Point95.2%Its own PINT benchmark. Source

Not published: Prompt Shields, Bedrock Guardrails, Model Armor, Lasso for Claude Code, Prisma AIRS for Claude Code, Snyk Studio hooks, AI Guard for Claude Code. Each vendor tests on its own set, so read these as published claims side by side.

Time added to a promptLower is better
  1. Lakera GuardCheck PointUnder 40 msShort prompts, setup not published. Source
  2. LLM GuardProtect AI104 msOn a CPU; 7.65 ms on a GPU. Source
  3. Kriton ShieldKriton341 msMedian of 210 decisions, our side only. Run file on request
  4. NeMo GuardrailsNVIDIA530 msAverage added with three safety models. Source

Not published: Prompt Shields, Bedrock Guardrails, Model Armor, Lasso for Claude Code, Prisma AIRS for Claude Code, Snyk Studio hooks, AI Guard for Claude Code. Ours is the decision on our side, before network time. Vendors measured on their own setups.

07Pilot

Start taking command of your agents now.

We reply by email with times for a call.

  • You see it stop a tricked agent on our demo company first.
  • Then it runs on your folders, tools & infra, on the systems you pick.
  • Your security team can audit the product anytime under NDA.
People on your team using AI agents